

Integration set-up guide for Lever
September 27, 2023
To connect your customers' Lever accounts to your product through Unified.to, activate Lever in your Unified.to workspace, choose how customers authorize (Lever OAuth 2 with your own Lever client ID and secret, or a Lever API key each customer creates), embed the Authorization component, and save the connection ID each customer creates. As of 21 October 2026, Lever issues OAuth client IDs and secrets only to approved Lever partners, so teams without a partnership connect customers with Lever API keys. Your code then reads and writes Lever candidates, applications, jobs, notes and users through Unified.to's ATS and HR & Directory APIs.
This guide covers each step, from activation to your first API call, and what Unified.to's Lever integration supports.
Which authorization method should you use for Lever?
Use Lever OAuth 2 if you're an approved Lever partner, and Lever API keys if you're not. As of 21 October 2026, Lever says "As of 2020, all Lever integrations are authenticated using OAuth" and doesn't provide API keys for partner development (Lever OAuth documentation). Customers can still create API keys in their own Lever account. Unified.to's Lever integration offers both methods (Lever integration page).
| Lever OAuth 2 | Lever API key | |
|---|---|---|
| Who issues the credential | Lever's team, after Lever approves you as a partner | A Super Admin in your customer's Lever account |
| What you add in Unified.to | Your Lever client ID and secret, when you activate Lever | Nothing; each customer enters their key in the Authorization component |
| Who approves access in Lever | A Lever Super Admin, for the whole Lever organization | The Super Admin who creates the key and chooses its permissions |
| Lever plan requirement (as of 21 October 2026) | Available to all Lever customers | Customer needs Lever's Data API feature |
| As of 20 September 2026, Unified.to doesn't supply shared Lever OAuth credentials, so Lever OAuth 2 connections need your own Lever client ID and secret, which means your own Lever partnership. Plan and access rules are from Lever's partner process page, as of 21 October 2026. |
What do you need before you start?
You need a Unified.to account and one of the two Lever credentials above.
- Unified.to account: sign up at app.unified.to. Grow and Pro start with a 30-day free trial.
- For Lever OAuth 2: Lever partner approval and the client ID and secret Lever sends you (step 2).
- For Lever API keys: customers whose Lever plan includes the Data API feature, with a Super Admin who can create the key.
1. How do you activate Lever in Unified.to?
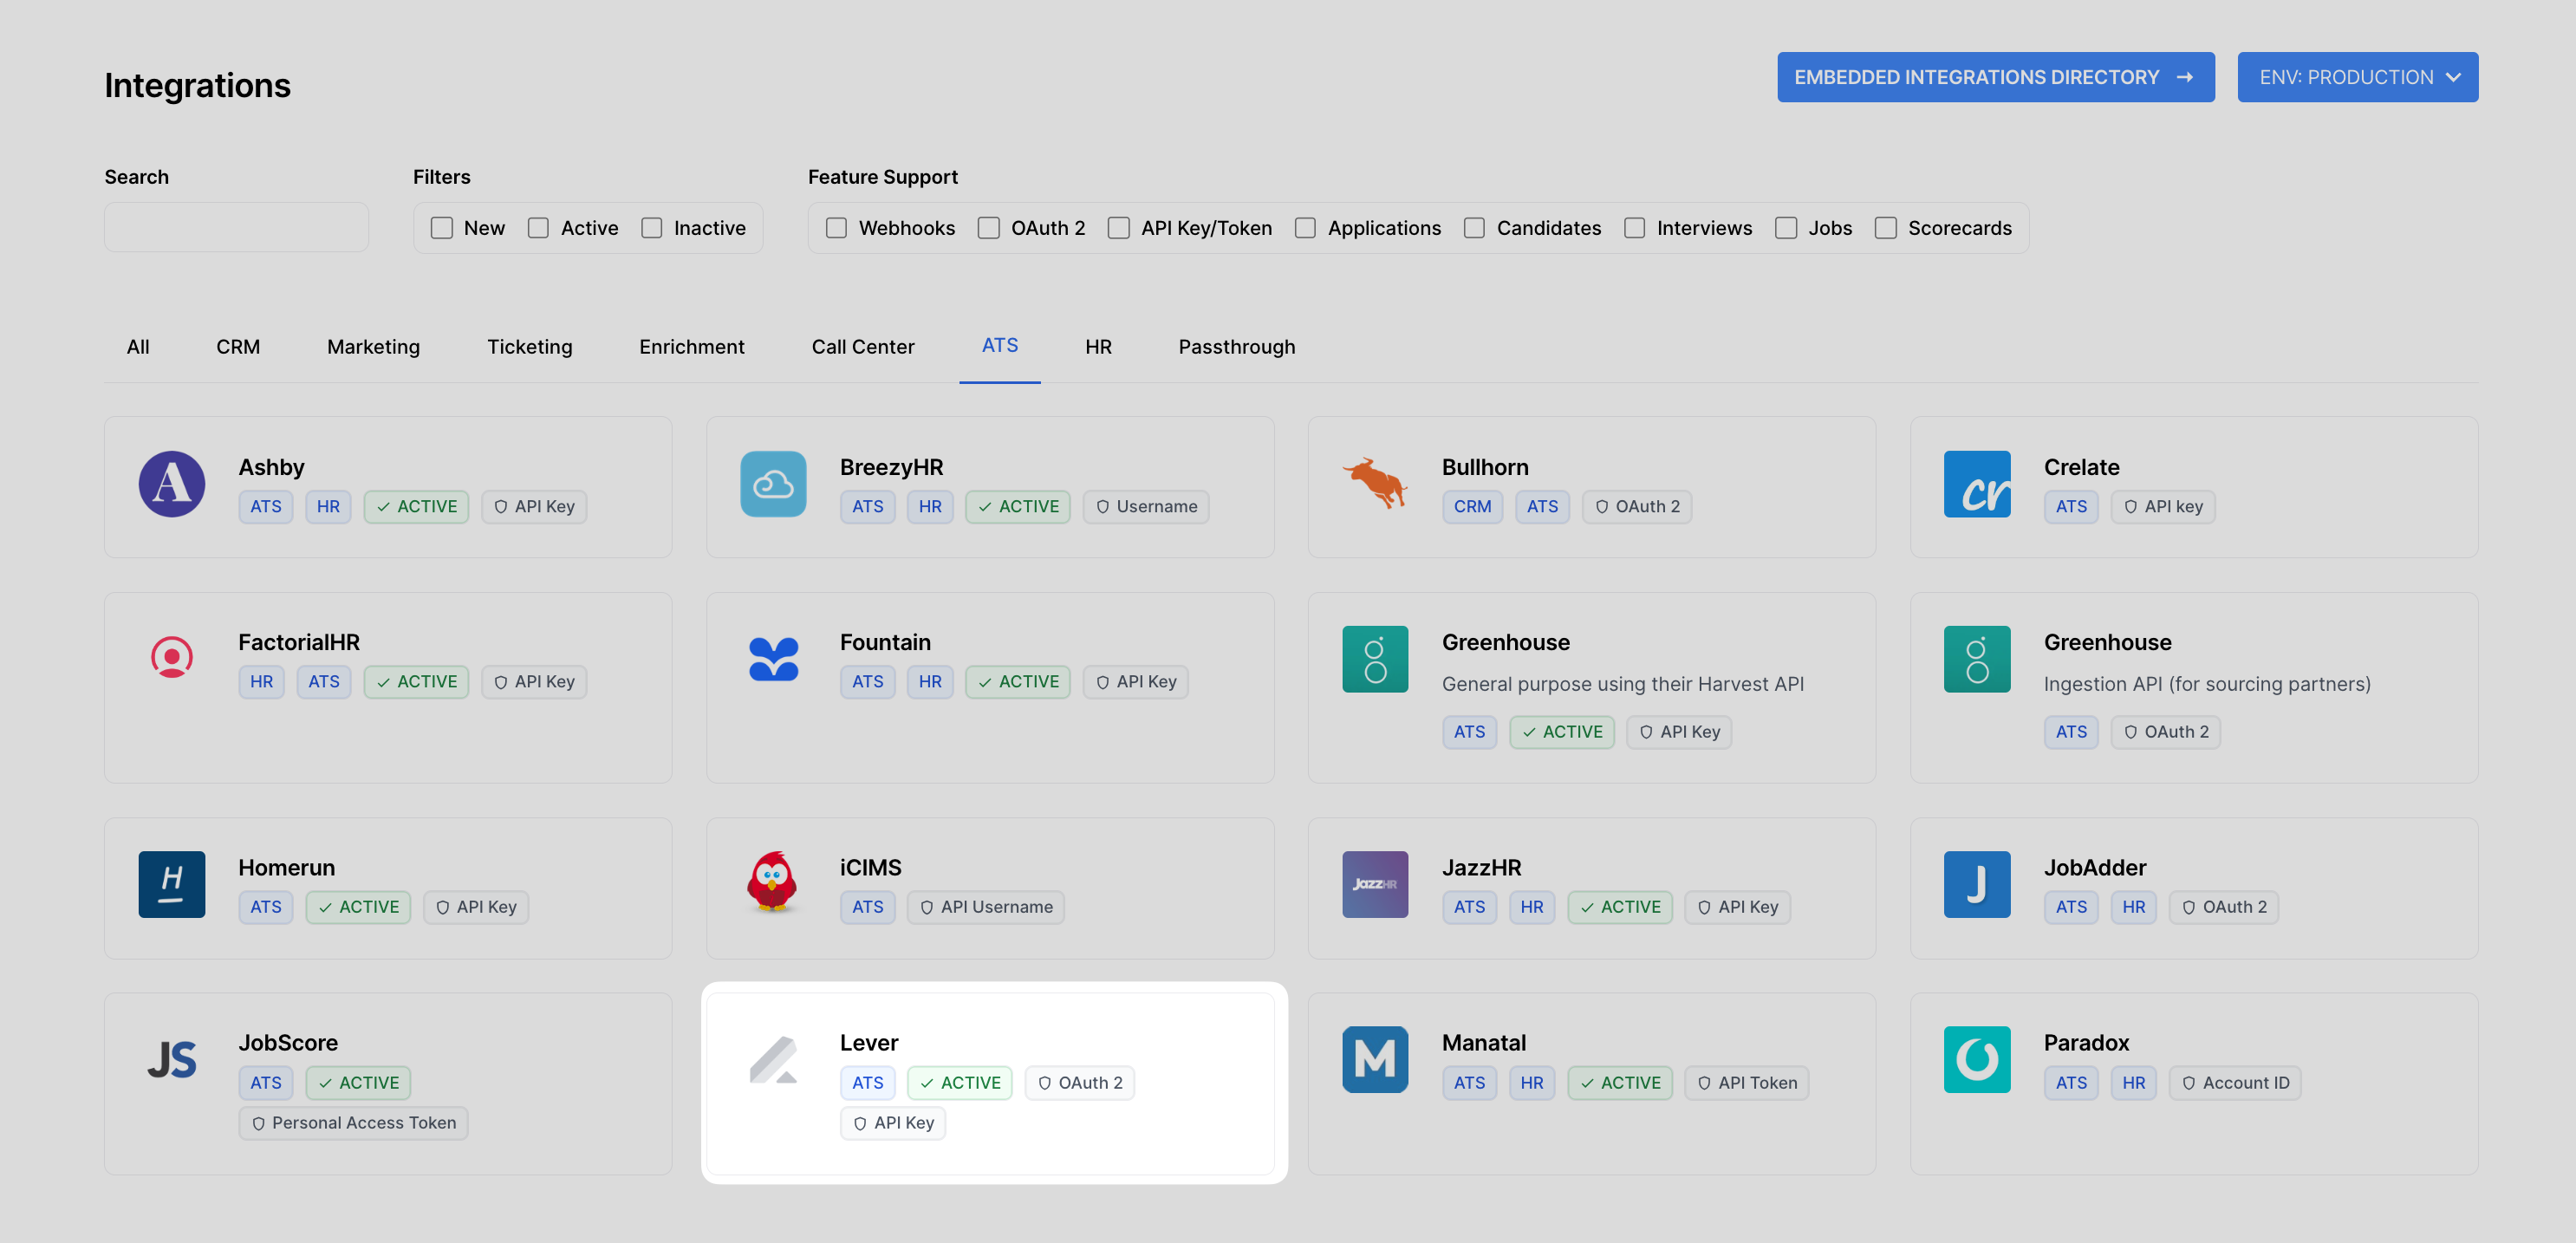
Open Integrations in Unified.to, search for Lever or filter by the ATS category, open the Lever card and select Activate. The integrations you activate are the ones your customers see in the Authorization component.
2. How do you get Lever OAuth 2 credentials?
Lever OAuth 2 credentials come only through Lever's partner program: as of 21 October 2026, "Someone on the Lever team will create your OAuth app and send over your ClientID and Secret" (Lever partner process). Unified.to has no shared Lever OAuth app, so this step is required for Lever OAuth 2. Skip it only if your customers will connect with API keys.
- Tell Lever you want to build an integration, using Lever's partnership interest form. Lever's partnerships team reviews each request.
- Once Lever approves you, it provides a Lever sandbox account. Email is turned off in the sandbox, so invited users sign in through the login link.
- Register your sandbox OAuth app (fields below). Lever's team creates it and sends the client ID and secret.
- Build and test against the sandbox, then send Lever its four packages: a help centre article about your integration, two sandbox logins for Lever (sadmin@levertest.com and integration-support@lever.co), listing information and technical support details.
- After a QA run-through, where you share your screen and walk through the full connection journey, Lever provides production OAuth credentials.
What does Lever ask for when you register the app?
Lever asks for an integration name, a description of 20 to 140 characters, a callback URI, a link to a square logo (150 × 150 px recommended; not a Google Drive or download link) and the scopes you need (Lever OAuth documentation, as of 21 October 2026). Lever's scope rules:
- Most use cases need 5 to 8 scopes, and the maximum is 20.
- A
write:adminscope includes itsread:adminscope, so register only the write scope when you need both. - Include
offline_access. Without it, Lever issues no refresh token.
As of 20 September 2026, Unified.to's Lever integration requests offline_access plus Lever scopes for opportunities, contact, resumes, postings, users, interviews, stages, files, notes and webhooks, at read or write level depending on the Unified.to objects you use (Lever OAuth app skill). Register those resources with Lever, using the write:admin form for any object you create, update or remove: that's 11 scopes, within Lever's limit of 20. Unified.to doesn't request Lever's confidential:access:admin scope. See Understanding scopes.
Which callback URI do you give Lever?
Give Lever the Unified.to callback URI for your workspace's region. Each workspace has one region: US on every plan, EU or AU on Pro and Scale.
| Unified.to workspace region | Callback URI |
|---|---|
| US (every plan) | https://api.unified.to/oauth/code |
| EU (Pro and Scale) | https://api-eu.unified.to/oauth/code |
| AU (Pro and Scale) | https://api-au.unified.to/oauth/code |
Copy the URI exactly: a trailing slash, the wrong subdomain or http instead of https makes the connection fail. As of 21 October 2026, Lever requires the callback you use to match one registered with your app, and callbacks can't differ per customer. Lever's OAuth page says you register with one callback and request more through Lever support, and its FAQ says an app can have several, so list every region you need when you register. Lever's sandbox and production apps are separate, each with its own client ID, secret and callbacks. |
3. Where do you enter the Lever client ID and secret?
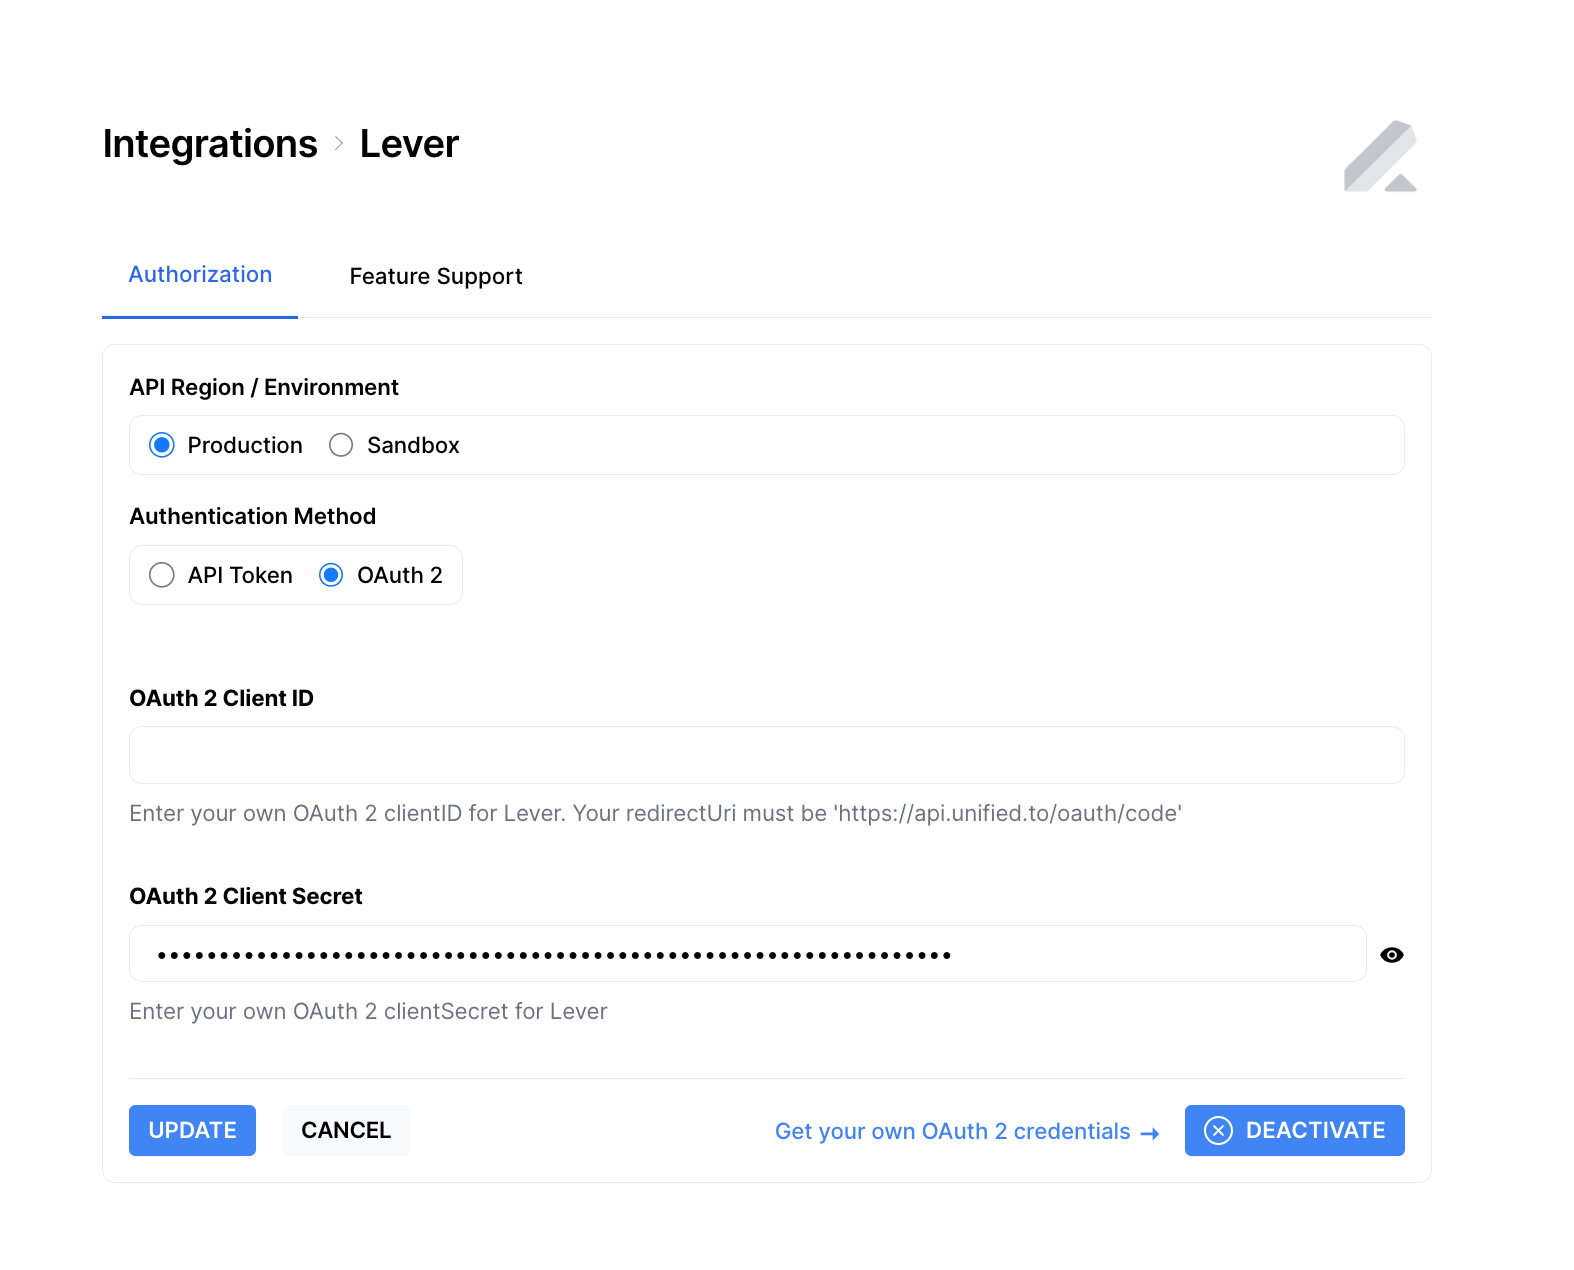
On the Lever card in Unified.to, select Your OAuth 2 credentials, enter the Lever client ID and secret, and select Activate. To test against your Lever sandbox, select Sandbox on the card and enter the sandbox app's client ID and secret; Lever's sandbox and production credentials aren't interchangeable.
Lever's sandbox is a real Lever account for partners. Unified.to's own Sandbox (synthetic data) environment is different: it returns synthetic data and accepts any value as credentials (Sandbox).
When a customer connects, a Lever Super Admin approves your app for their whole Lever organization (Lever, as of 21 October 2026). Unified.to keeps no customer records at rest; connection credentials and operational metadata are encrypted at rest.
How do your customers create a Lever API key?
A Super Admin in your customer's Lever account creates the key under Settings > Integrations and API > API Credentials, then enters it when they choose Lever in your Authorization component (Lever API documentation and developer FAQ, as of 21 October 2026).
- Select Generate New Key and name the key after your product.
- Under Permissions, choose Select all, as shown in How to get your Lever API key. Lever checks every call against the key's permissions, so a key missing one fails on that endpoint.
- If the customer wants confidential postings and opportunities included, grant confidential access now. Lever allows it only when the key is created.
- Copy the key and paste it into your Authorization component.
Lever API keys "carry many privileges, so keep them secret", and a Lever account can have several active keys, so each product can have its own. Step-by-step screenshots: How to get your Lever API key.
What if your customer's Lever account is hosted in the EU?
Lever hosts some accounts in the EU, at hire.eu.lever.co instead of hire.lever.co. EU-hosted accounts use separate Lever servers, so the customer needs to choose the EU environment when they connect Lever in your Authorization component.
- The customer creates their API key at
hire.eu.lever.co, under Settings > Integrations and API > API Credentials, following the same steps above. - EU-hosted Lever accounts currently connect with API keys only. Lever OAuth 2 isn't available for EU accounts yet.
- The EU environment refers to where the customer's Lever account is hosted. It's separate from your Unified.to workspace region.
4. How do you add Lever to your app?
Add Unified.to's Authorization component to your product: your customers pick Lever, authorize, and return to your app with a connection ID.
- Copy your workspace ID from Settings > API Keys in Unified.to. You can create several environments in one workspace for testing, staging and production; see Set environments for your Unified.to workspace.
- Open app.unified.to/embed, copy the snippet and replace
YOUR_WORKSPACE_IDwith your workspace ID. The preview shows what your customers see. Components are also available for React, Angular, Vue and Svelte (embedded components). - To build your own UI instead, call
GET /unified/integration/workspace/{workspace_id}, which returns all activated integrations in a workspace, and show those integrations in your app. - After a customer authorizes, Unified.to returns them to your app with the connection ID in the URL (for example
?id={connection_id}). Store it with that customer's record (associate a connection ID with your end user).
5. How do you make your first Lever API call?
Call Unified.to's ATS endpoints with the customer's connection ID, for example GET /ats/{connection_id}/candidate to list Lever candidates. The same endpoints work for every ATS integration, so Lever calls differ from other ATS calls only by connection ID.
SDKs are available for TypeScript, Python, PHP, Java, Go, C# and Ruby (SDKs). To see the data model before a customer connects, add env=Sandbox to your API calls for synthetic data (Mock API server).
What can you do with a Lever connection?
As of 19 October 2026, Unified.to's Lever integration reads nine objects; it creates and updates candidates, applications, jobs, notes and users, adds documents, and removes candidates, documents, notes and interviews. It doesn't create or update interviews. Unified.to's candidate maps to Lever's opportunity, the object Lever has recommended since it deprecated its /candidates endpoints in 2020 (Lever API documentation, as of 21 October 2026). A Lever contact can have more than one opportunity, so a person with two Lever candidacies appears as two Unified.to candidates. Each Lever opportunity carries at most one application.
| Unified.to object | Lever object | Methods | Change events |
|---|---|---|---|
| ATS candidate | Opportunity | List, Get, Create, Update, Remove | Created: virtual. Updated: native and virtual. Deleted: native |
| ATS application | Opportunity posting stage | List, Get, Create, Update | Created: native and virtual. Updated: virtual |
| ATS job | Posting | List, Get, Create, Update | Created, updated: virtual |
| ATS interview | Opportunity interview | List, Get, Remove | Created, updated: native and virtual. Deleted: native |
| ATS document | Opportunity file | List, Get, Create, Remove | Created, updated: virtual |
| ATS activity | Opportunity note | List, Get, Create, Update, Remove | None |
| ATS scorecard | Opportunity feedback | List, Get | Created, updated: virtual |
| ATS application status | Stage | List | None |
| HR & Directory employee | User | List, Get, Create, Update | Created, updated: virtual |
| Passthrough | Any Lever API endpoint | GET, POST, PUT, DELETE | None |
| Lever is one of 186 ATS integrations on Unified.to. Field-level detail is on the Lever integration page and in the ATS API overview. |
How do Lever changes reach your app?
Unified.to delivers Lever changes to your webhook URL in two ways. Native webhooks forward the events Lever sends: candidate updates and deletions, new applications, and interview changes. Virtual webhooks detect changes at an interval you set, as often as every minute on paid plans, and a check that finds nothing isn't billed. Every other Lever object with change events in the table above uses virtual webhooks.
On Lever API-key connections, native webhooks need the customer's Lever plan to include Lever's Webhook feature. If Lever refuses the subscription, Unified.to marks the native webhook unhealthy and doesn't switch to virtual checks, so a webhook can be created and still receive no events. For API-key connections, check the webhook's health after you create it, or create a virtual webhook for candidate updates. On Lever OAuth 2 connections, include Lever's webhooks:read:admin and webhooks:write:admin scopes.
As of 21 October 2026, Lever labels its interview webhook events Beta (Lever API documentation). See Understanding virtual webhooks.
Which Lever limits should you plan for?
As of 21 October 2026, Lever's API documentation sets these limits:
- Rate limit: 10 requests per second per API key, with bursts up to 20 when Lever allows. Lever says these defaults aren't guaranteed and recommends exponential backoff.
- OAuth tokens: on Lever OAuth 2 connections, access tokens expire after one hour, and refresh tokens expire after one year or after 90 days without use. API-key connections use basic auth and have no tokens to expire. Unified.to refreshes OAuth tokens on a schedule, including on connections with no recent calls, and each refresh returns a new Lever refresh token, so an idle connection doesn't reach Lever's 90-day inactivity limit. If Lever rejects a connection's credentials, Unified.to marks the connection unhealthy and sends a
CONNECTION_UNHEALTHYevent, so you can ask the customer to re-authorize (troubleshoot unhealthy connections). - Confidential records: Lever returns confidential postings and opportunities only to credentials granted confidential access. Unified.to doesn't request Lever's
confidential:access:adminscope (as of 20 September 2026), so Lever OAuth 2 connections don't return confidential records. On an API key, a Super Admin can grant confidential access only when creating the key.
Where can you get help?
Email hello@unified.to or chat with the team on Discord.
Keep learning: